


Every AI app wants to read your files, query your database and call your APIs. Without a standard, each app wires up each tool by hand. The Model Context Protocol (MCP) is the standard.
Details here follow the protocol revision dated 2026-07-28. Check the current spec before you build.
1. One protocol instead of every app wiring every tool
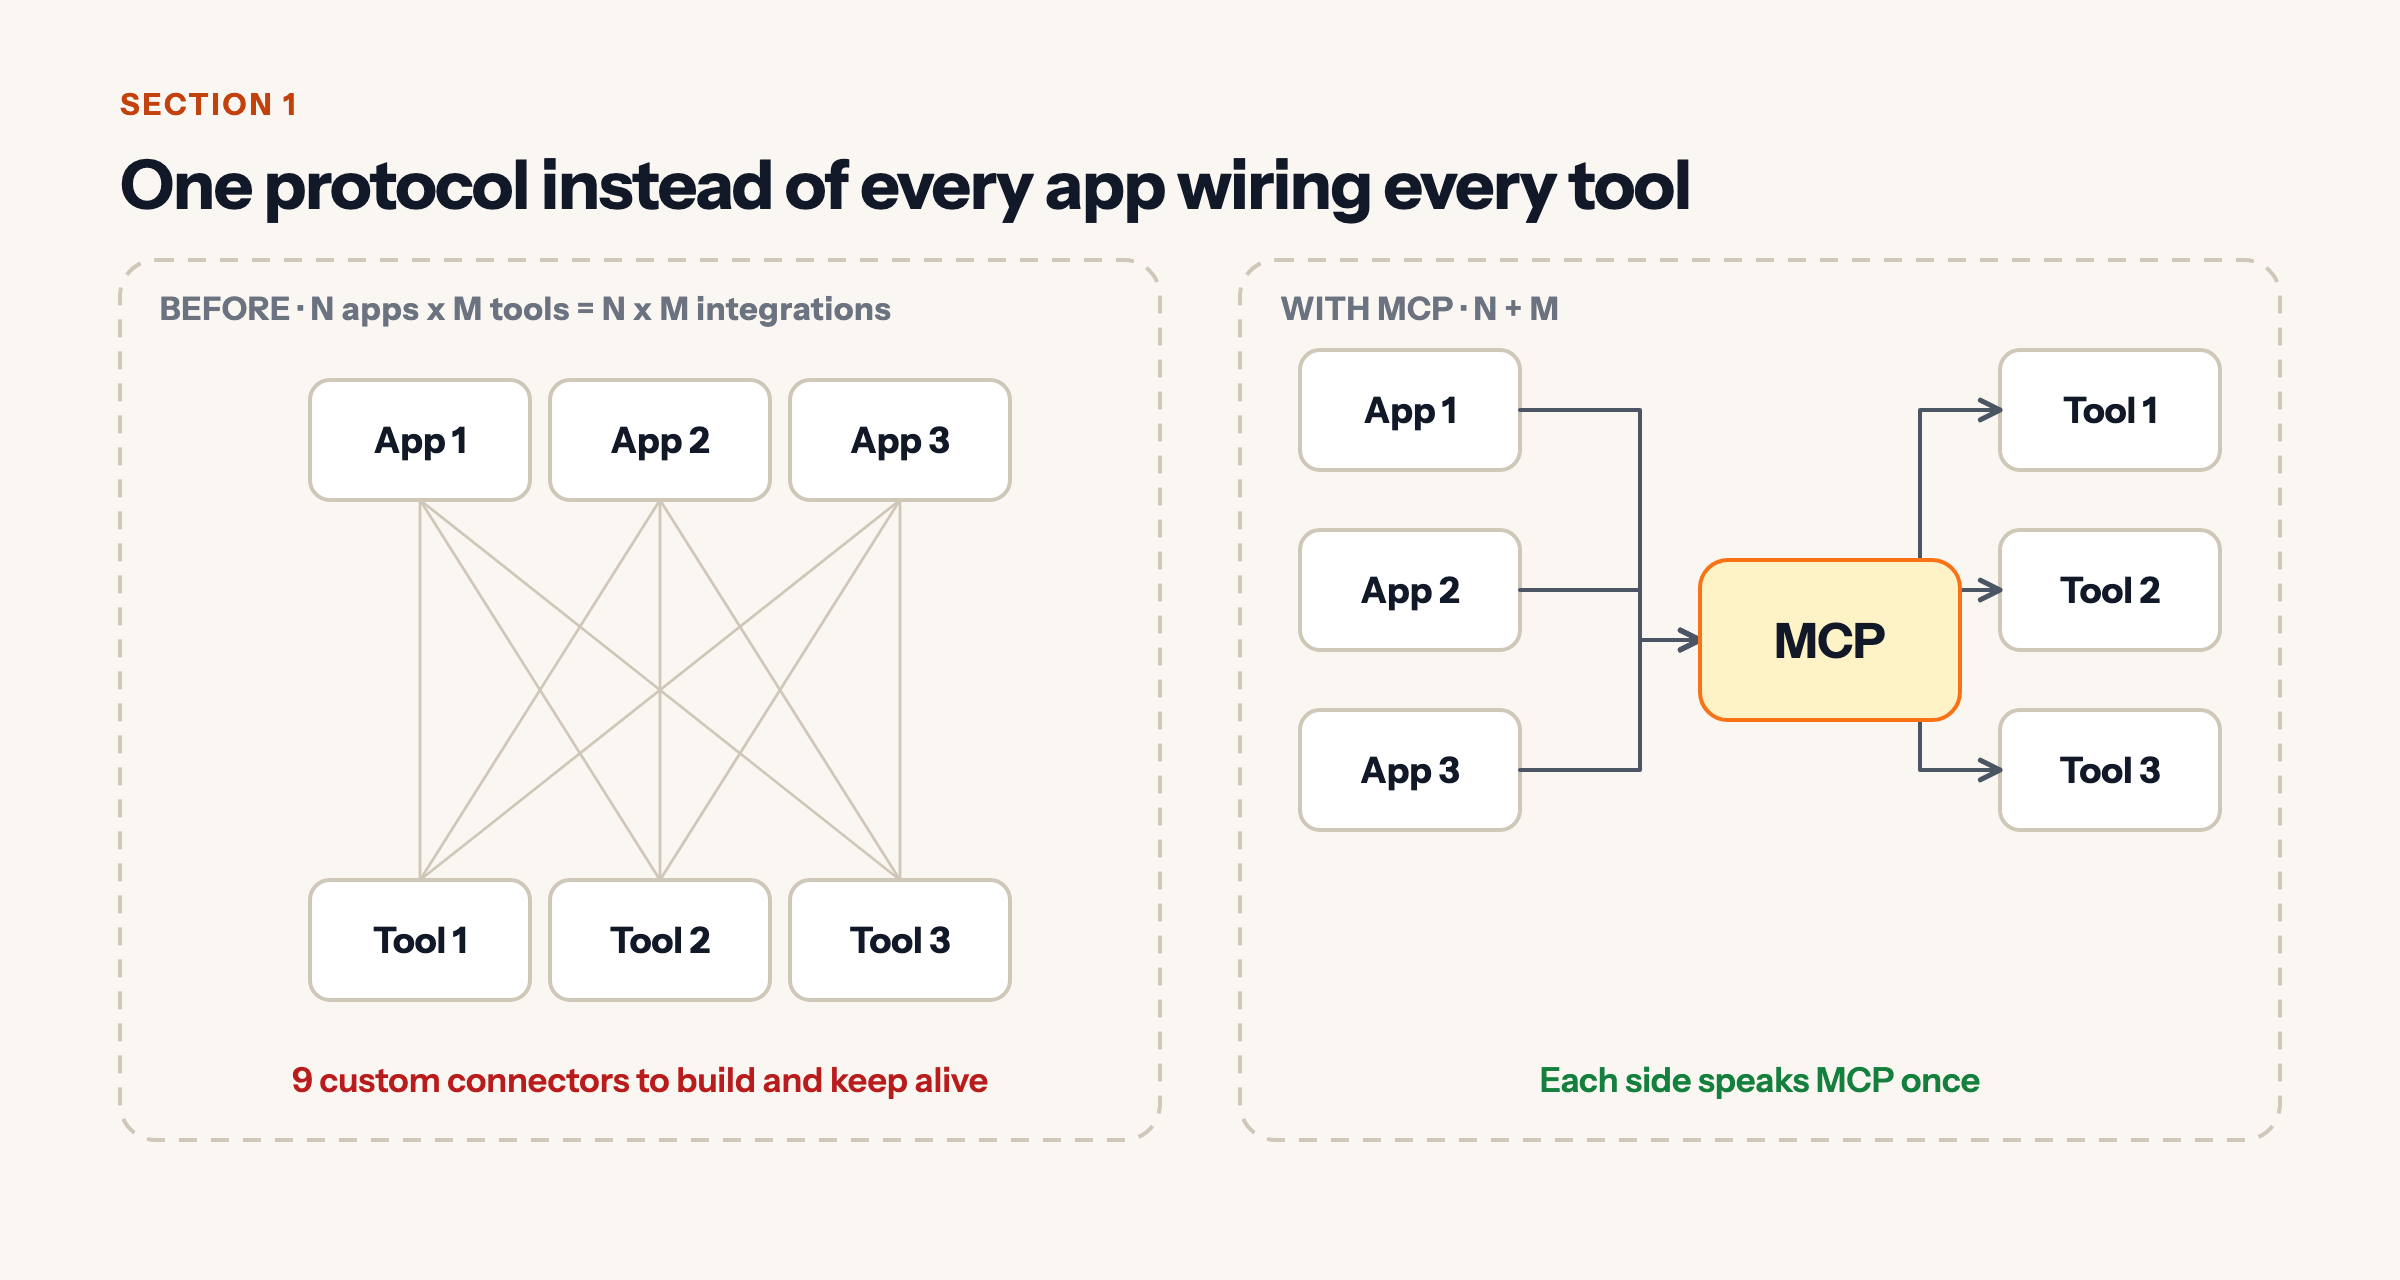
Without MCP, N apps and M tools mean N x M custom integrations. With MCP each side speaks the protocol once, so the work becomes N + M.

2. Host, clients and servers
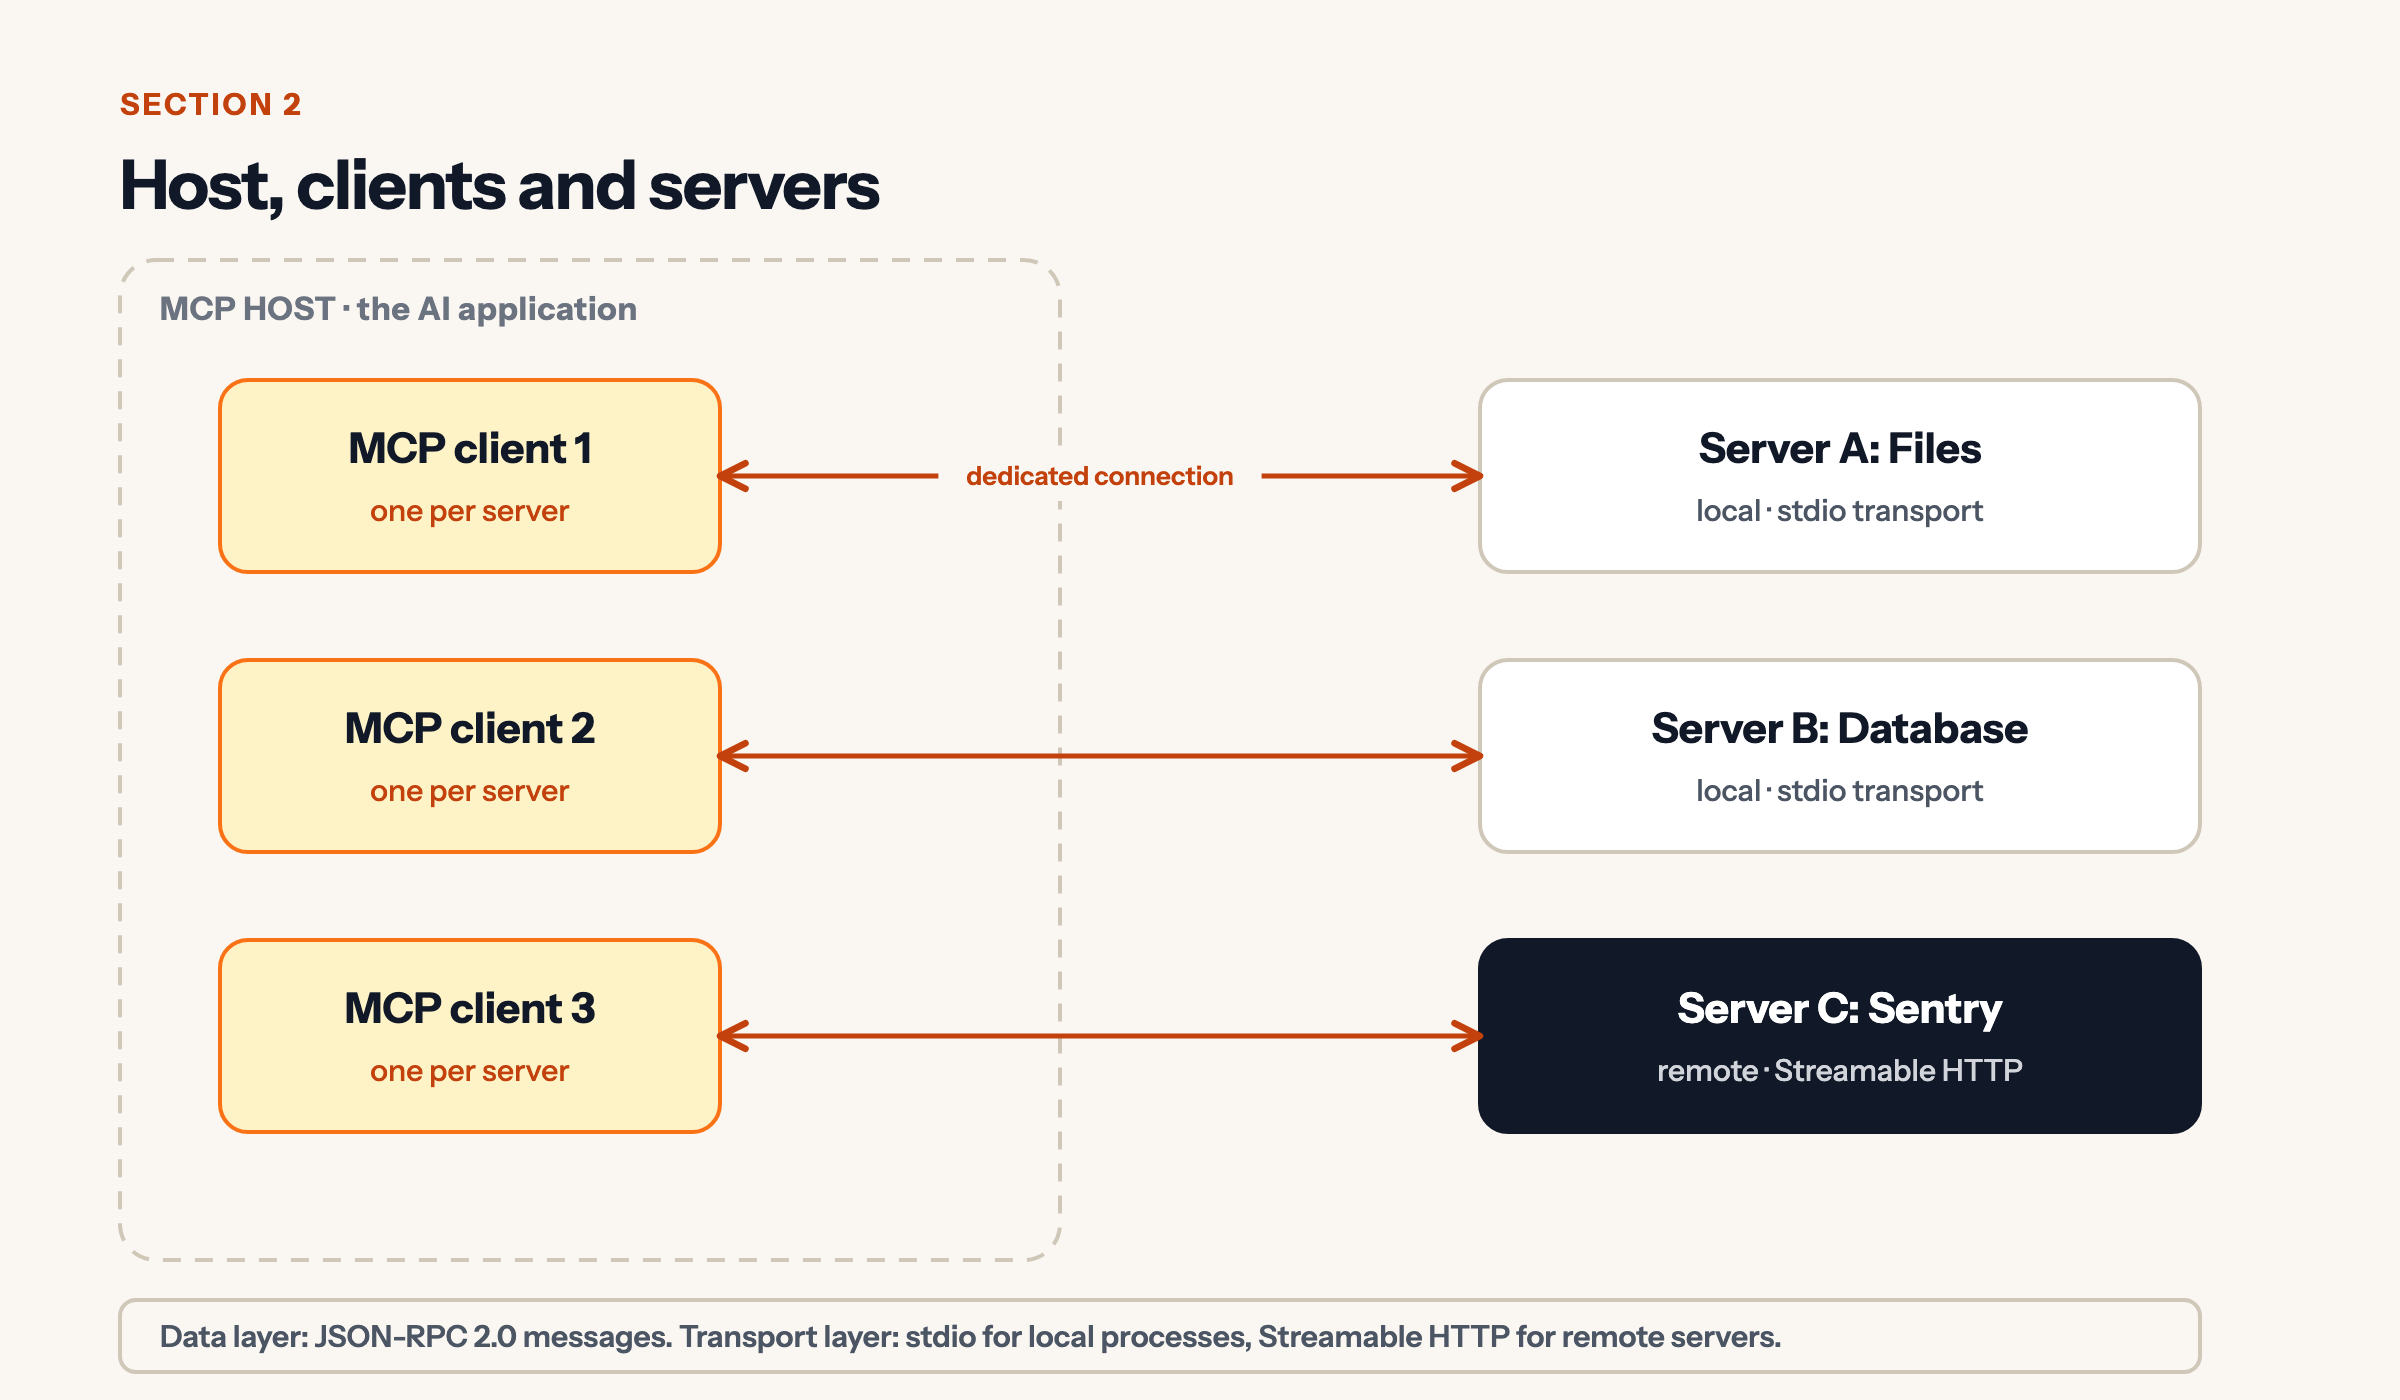
The host is the AI application. Inside it, one MCP client per server holds a dedicated connection. A server exposes capabilities, either locally over stdio or remotely over Streamable HTTP. Messages are JSON-RPC 2.0.

3. What a server can offer, and what a client can offer back
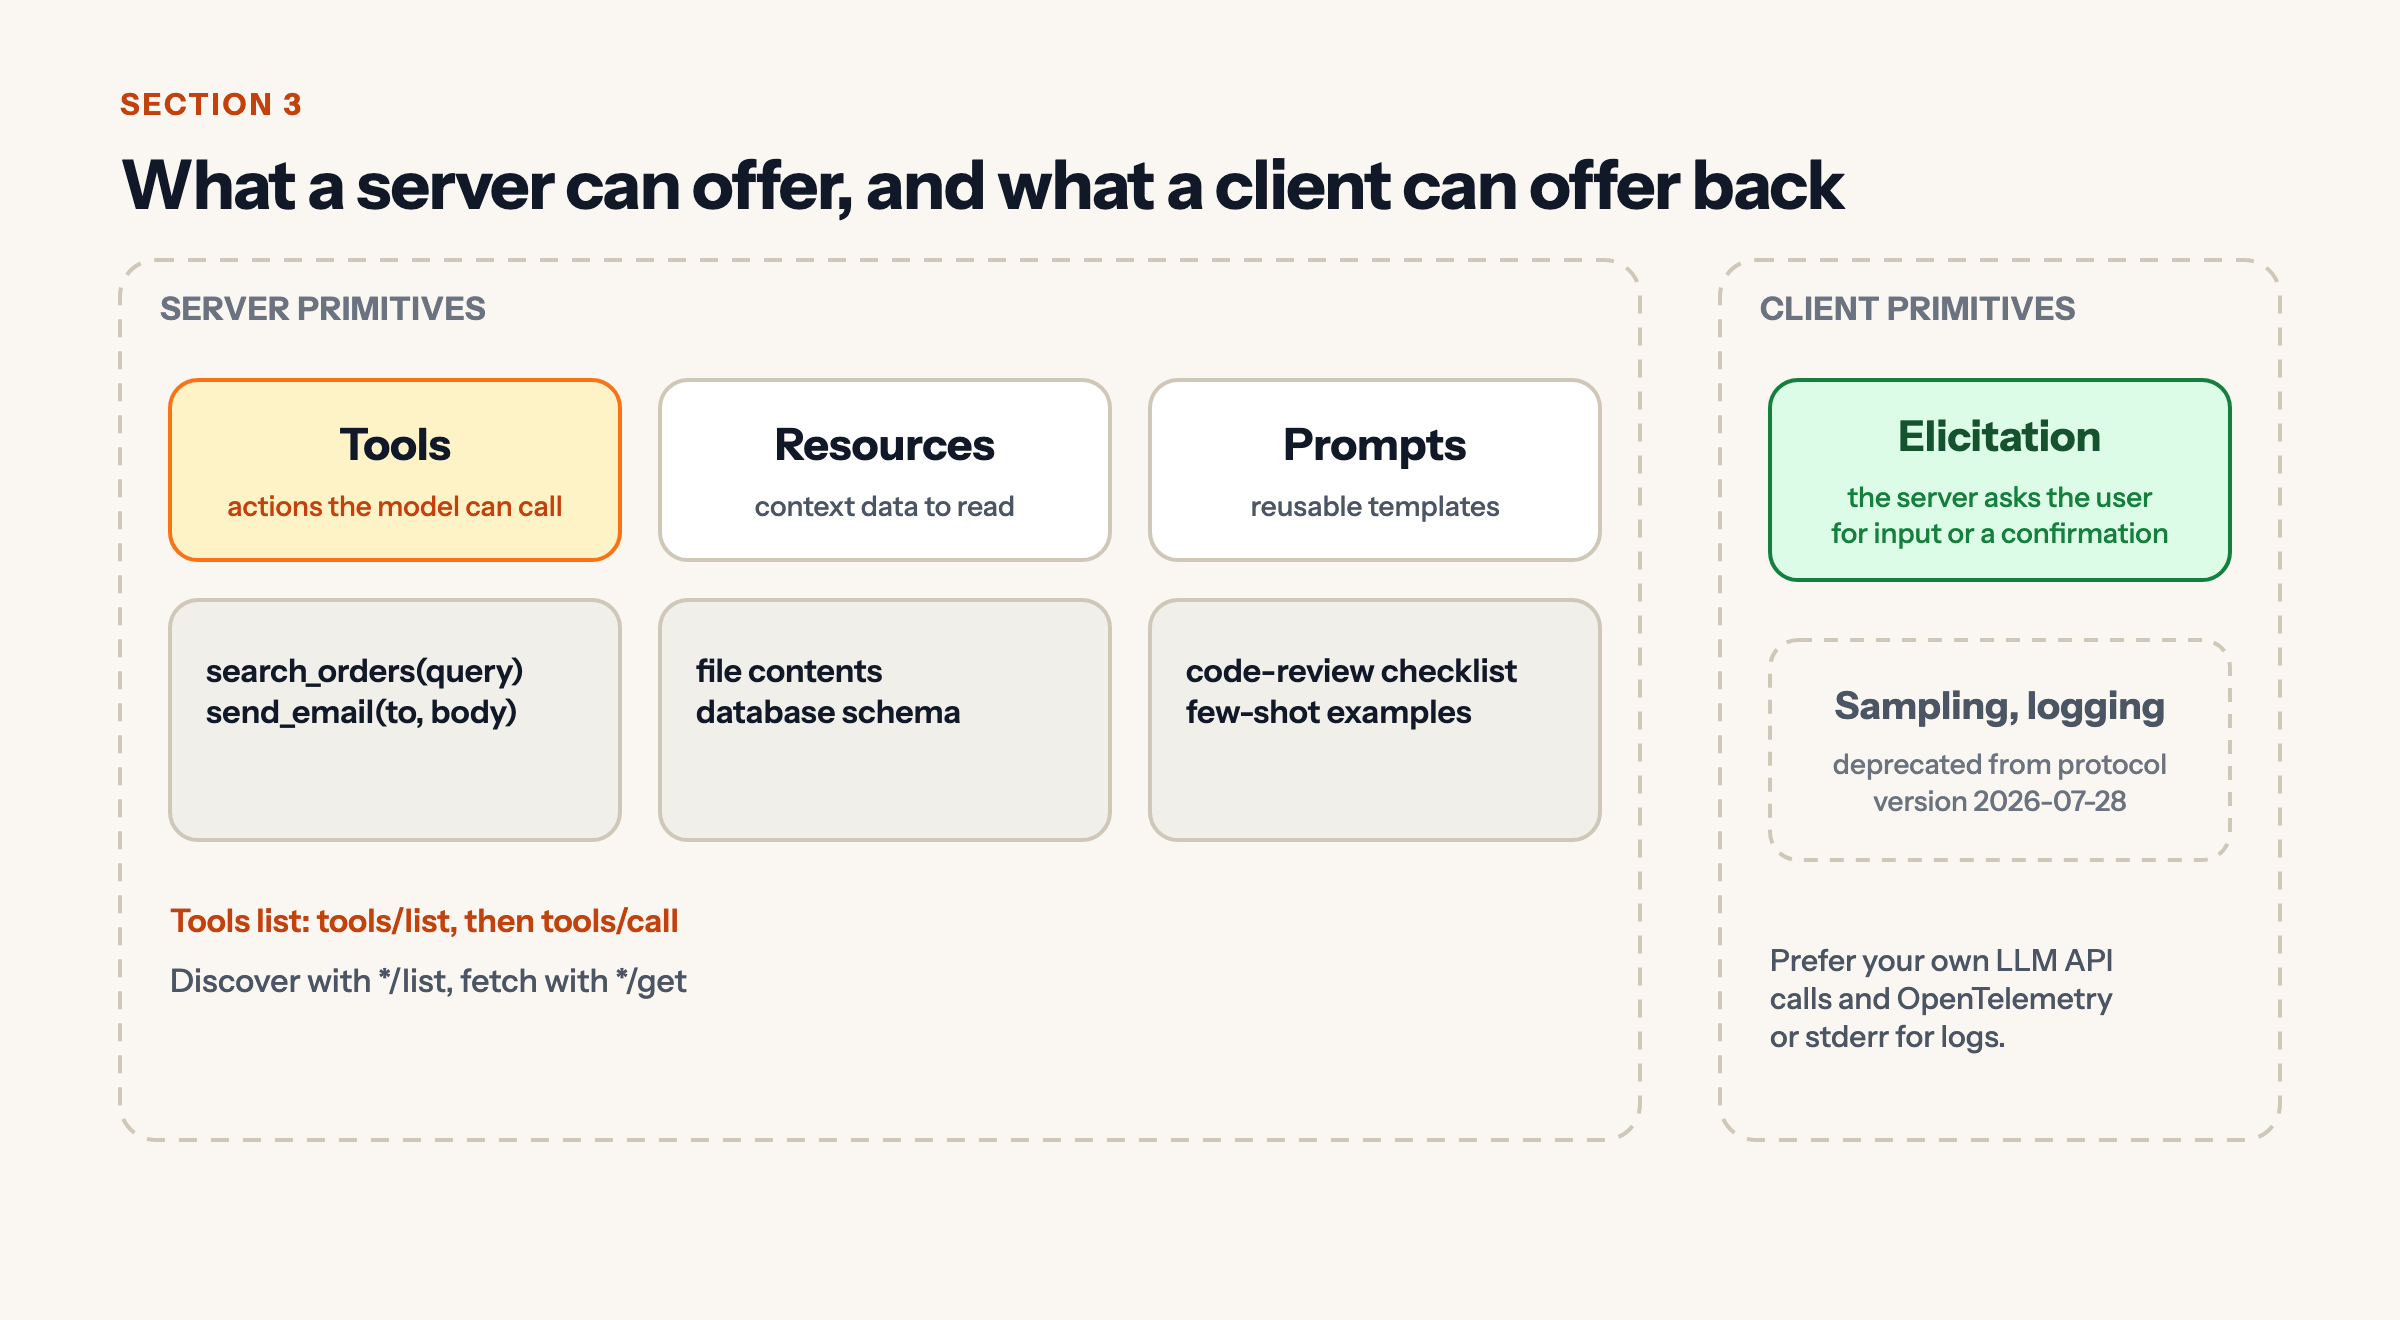
Servers offer three primitives.
- Tools: actions the model can call, such as
search_orders(query). - Resources: context data to read, such as file contents or a schema.
- Prompts: reusable templates.
Clients can offer elicitation, which lets a server ask the user for input or confirmation. Sampling and logging are deprecated from the 2026-07-28 revision; prefer your own LLM API calls, plus OpenTelemetry or stderr for logs.

4. A request, end to end
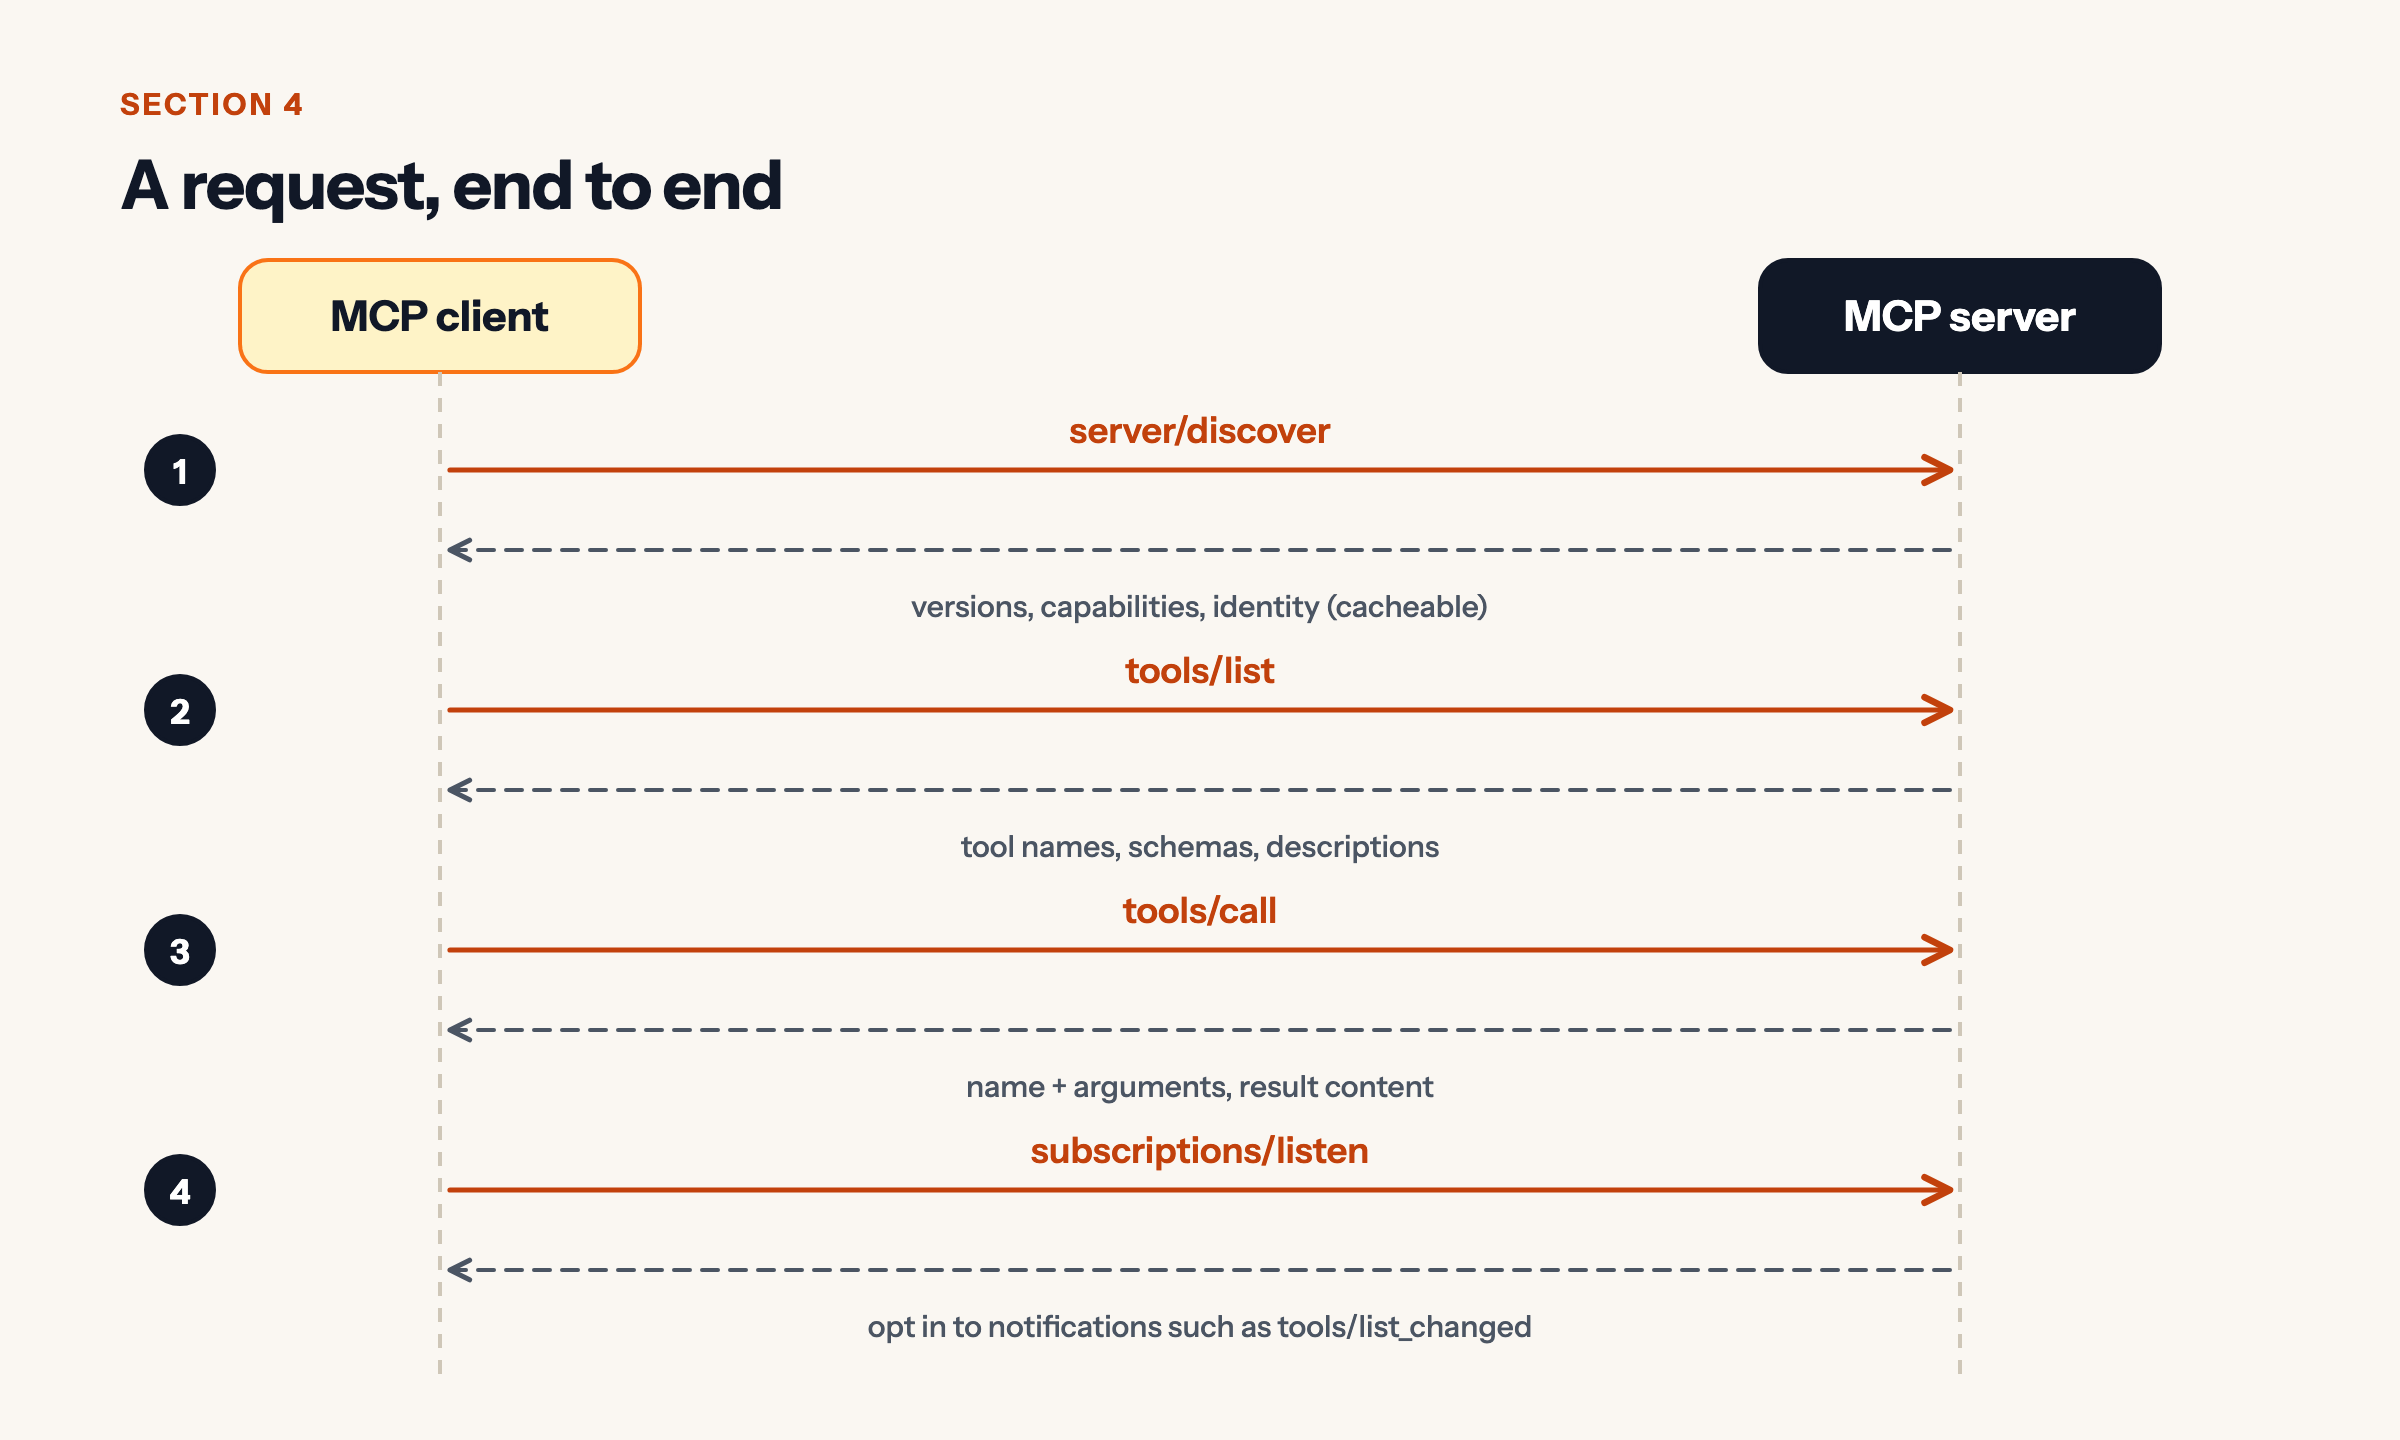
server/discover: the client learns versions, capabilities and identity, which can be cached.tools/list: the client gets tool names, schemas and descriptions.tools/call: the client sends a name and arguments and receives result content.subscriptions/listen: the client opts in to notifications such as a changed tool list.

5. From idea to a server your host can use
Write the server with an official SDK, starting with one small tool. Run it in the MCP Inspector and call it by hand. Add it to a host’s config, reviewing the exact command. Try real prompts and check the model picks the right tool. Then review scopes, errors and who called what.

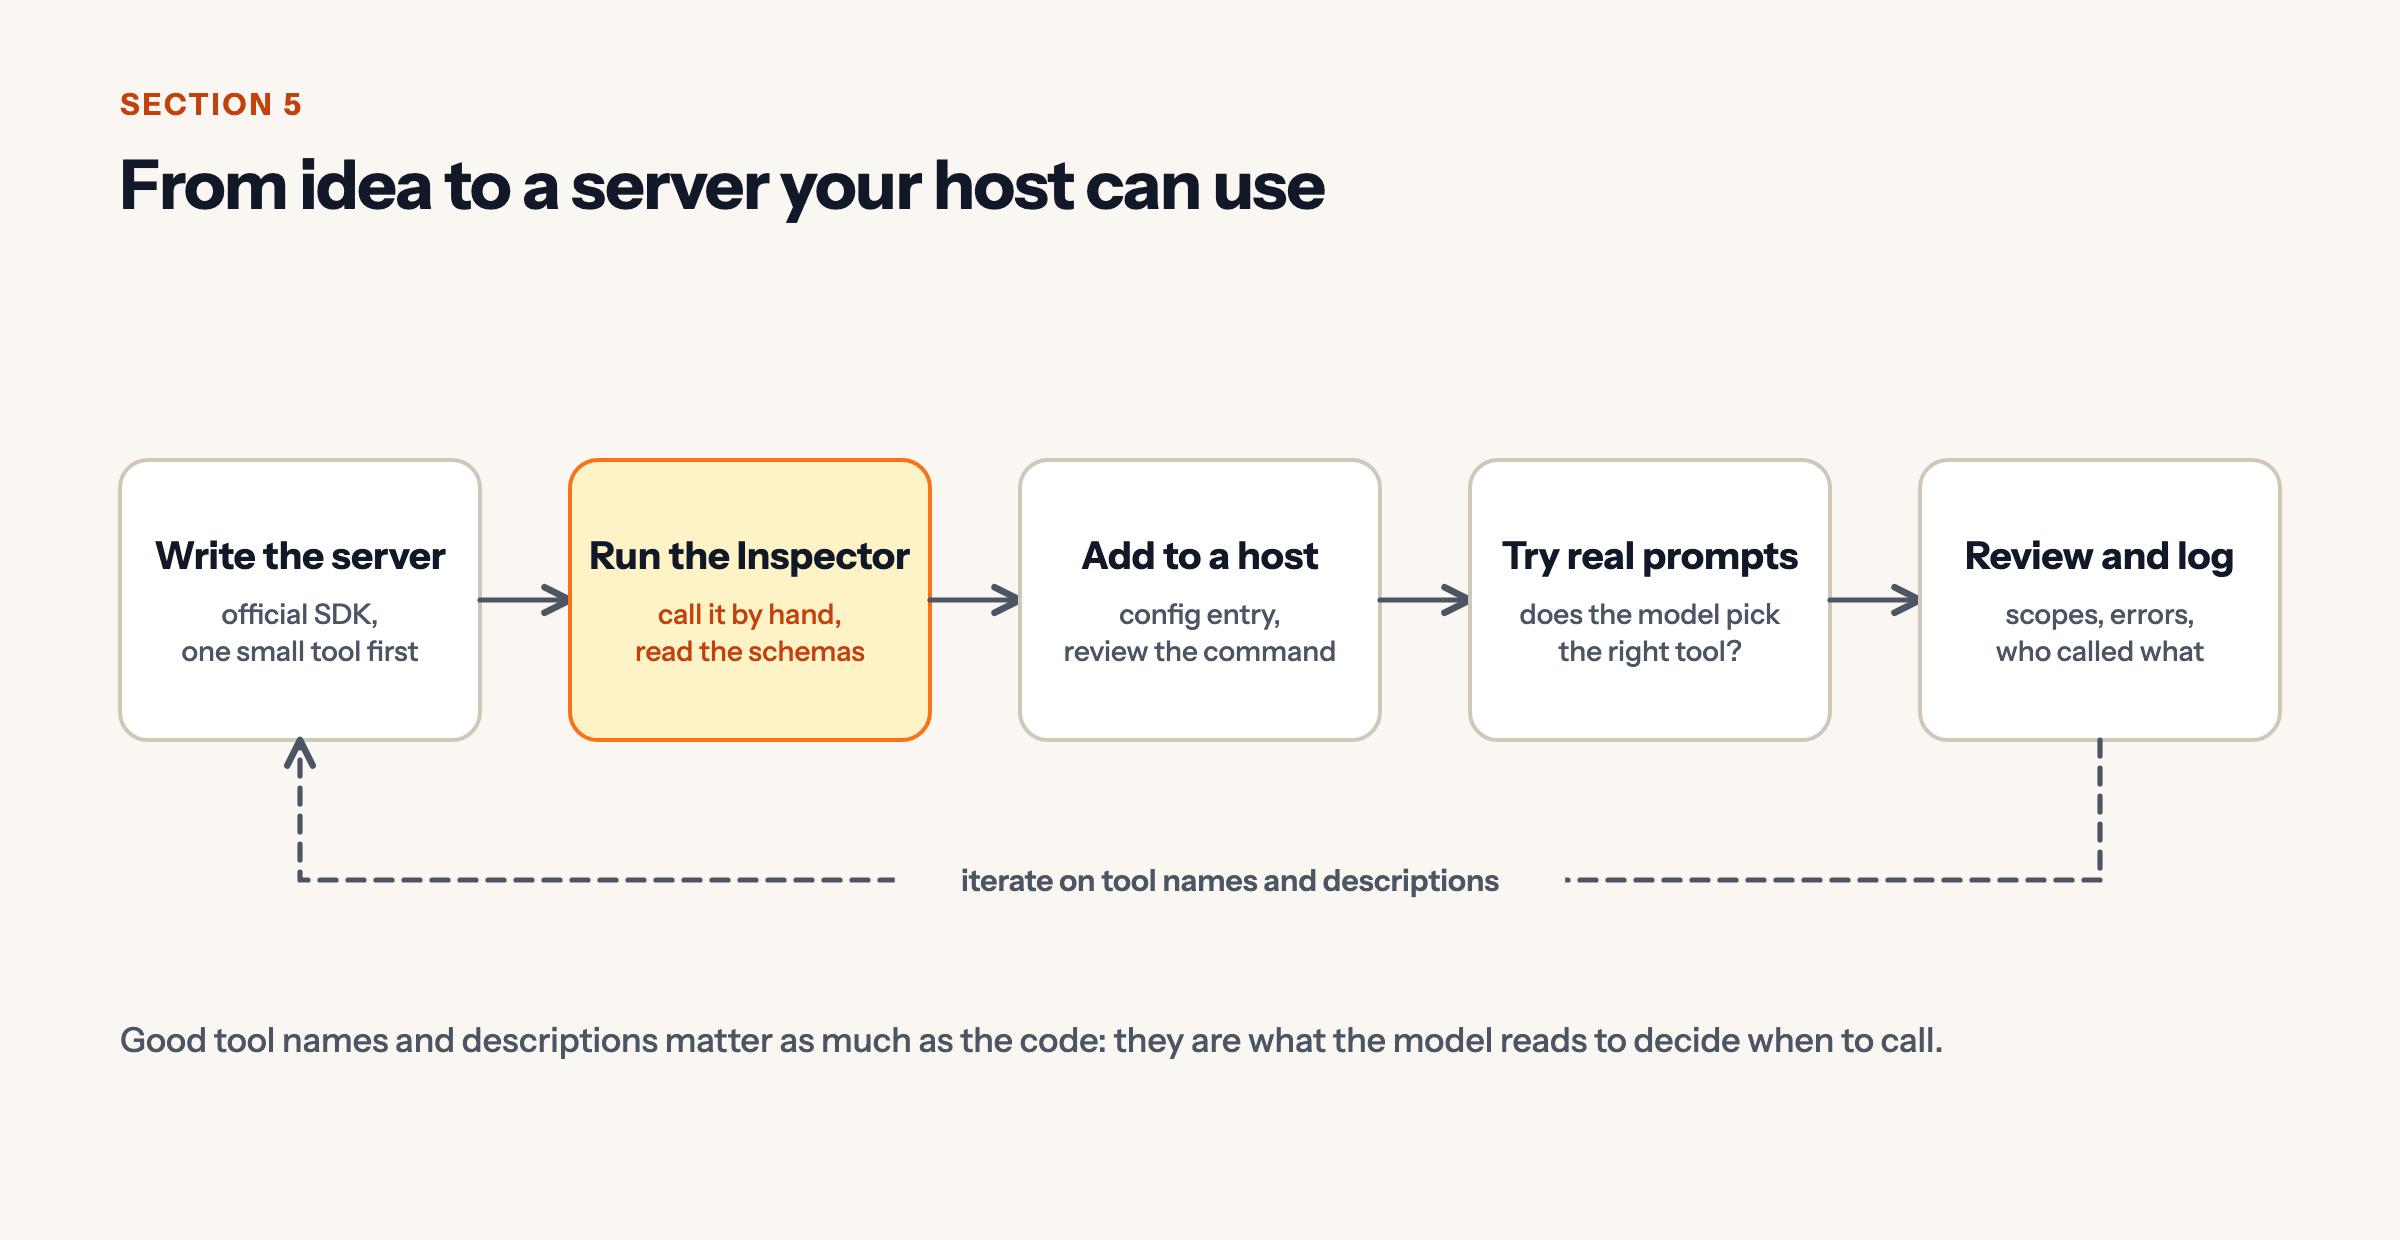
Tool names and descriptions matter as much as the code. They are what the model reads to decide when to call.
6. Six ways it goes wrong, and the fix for each

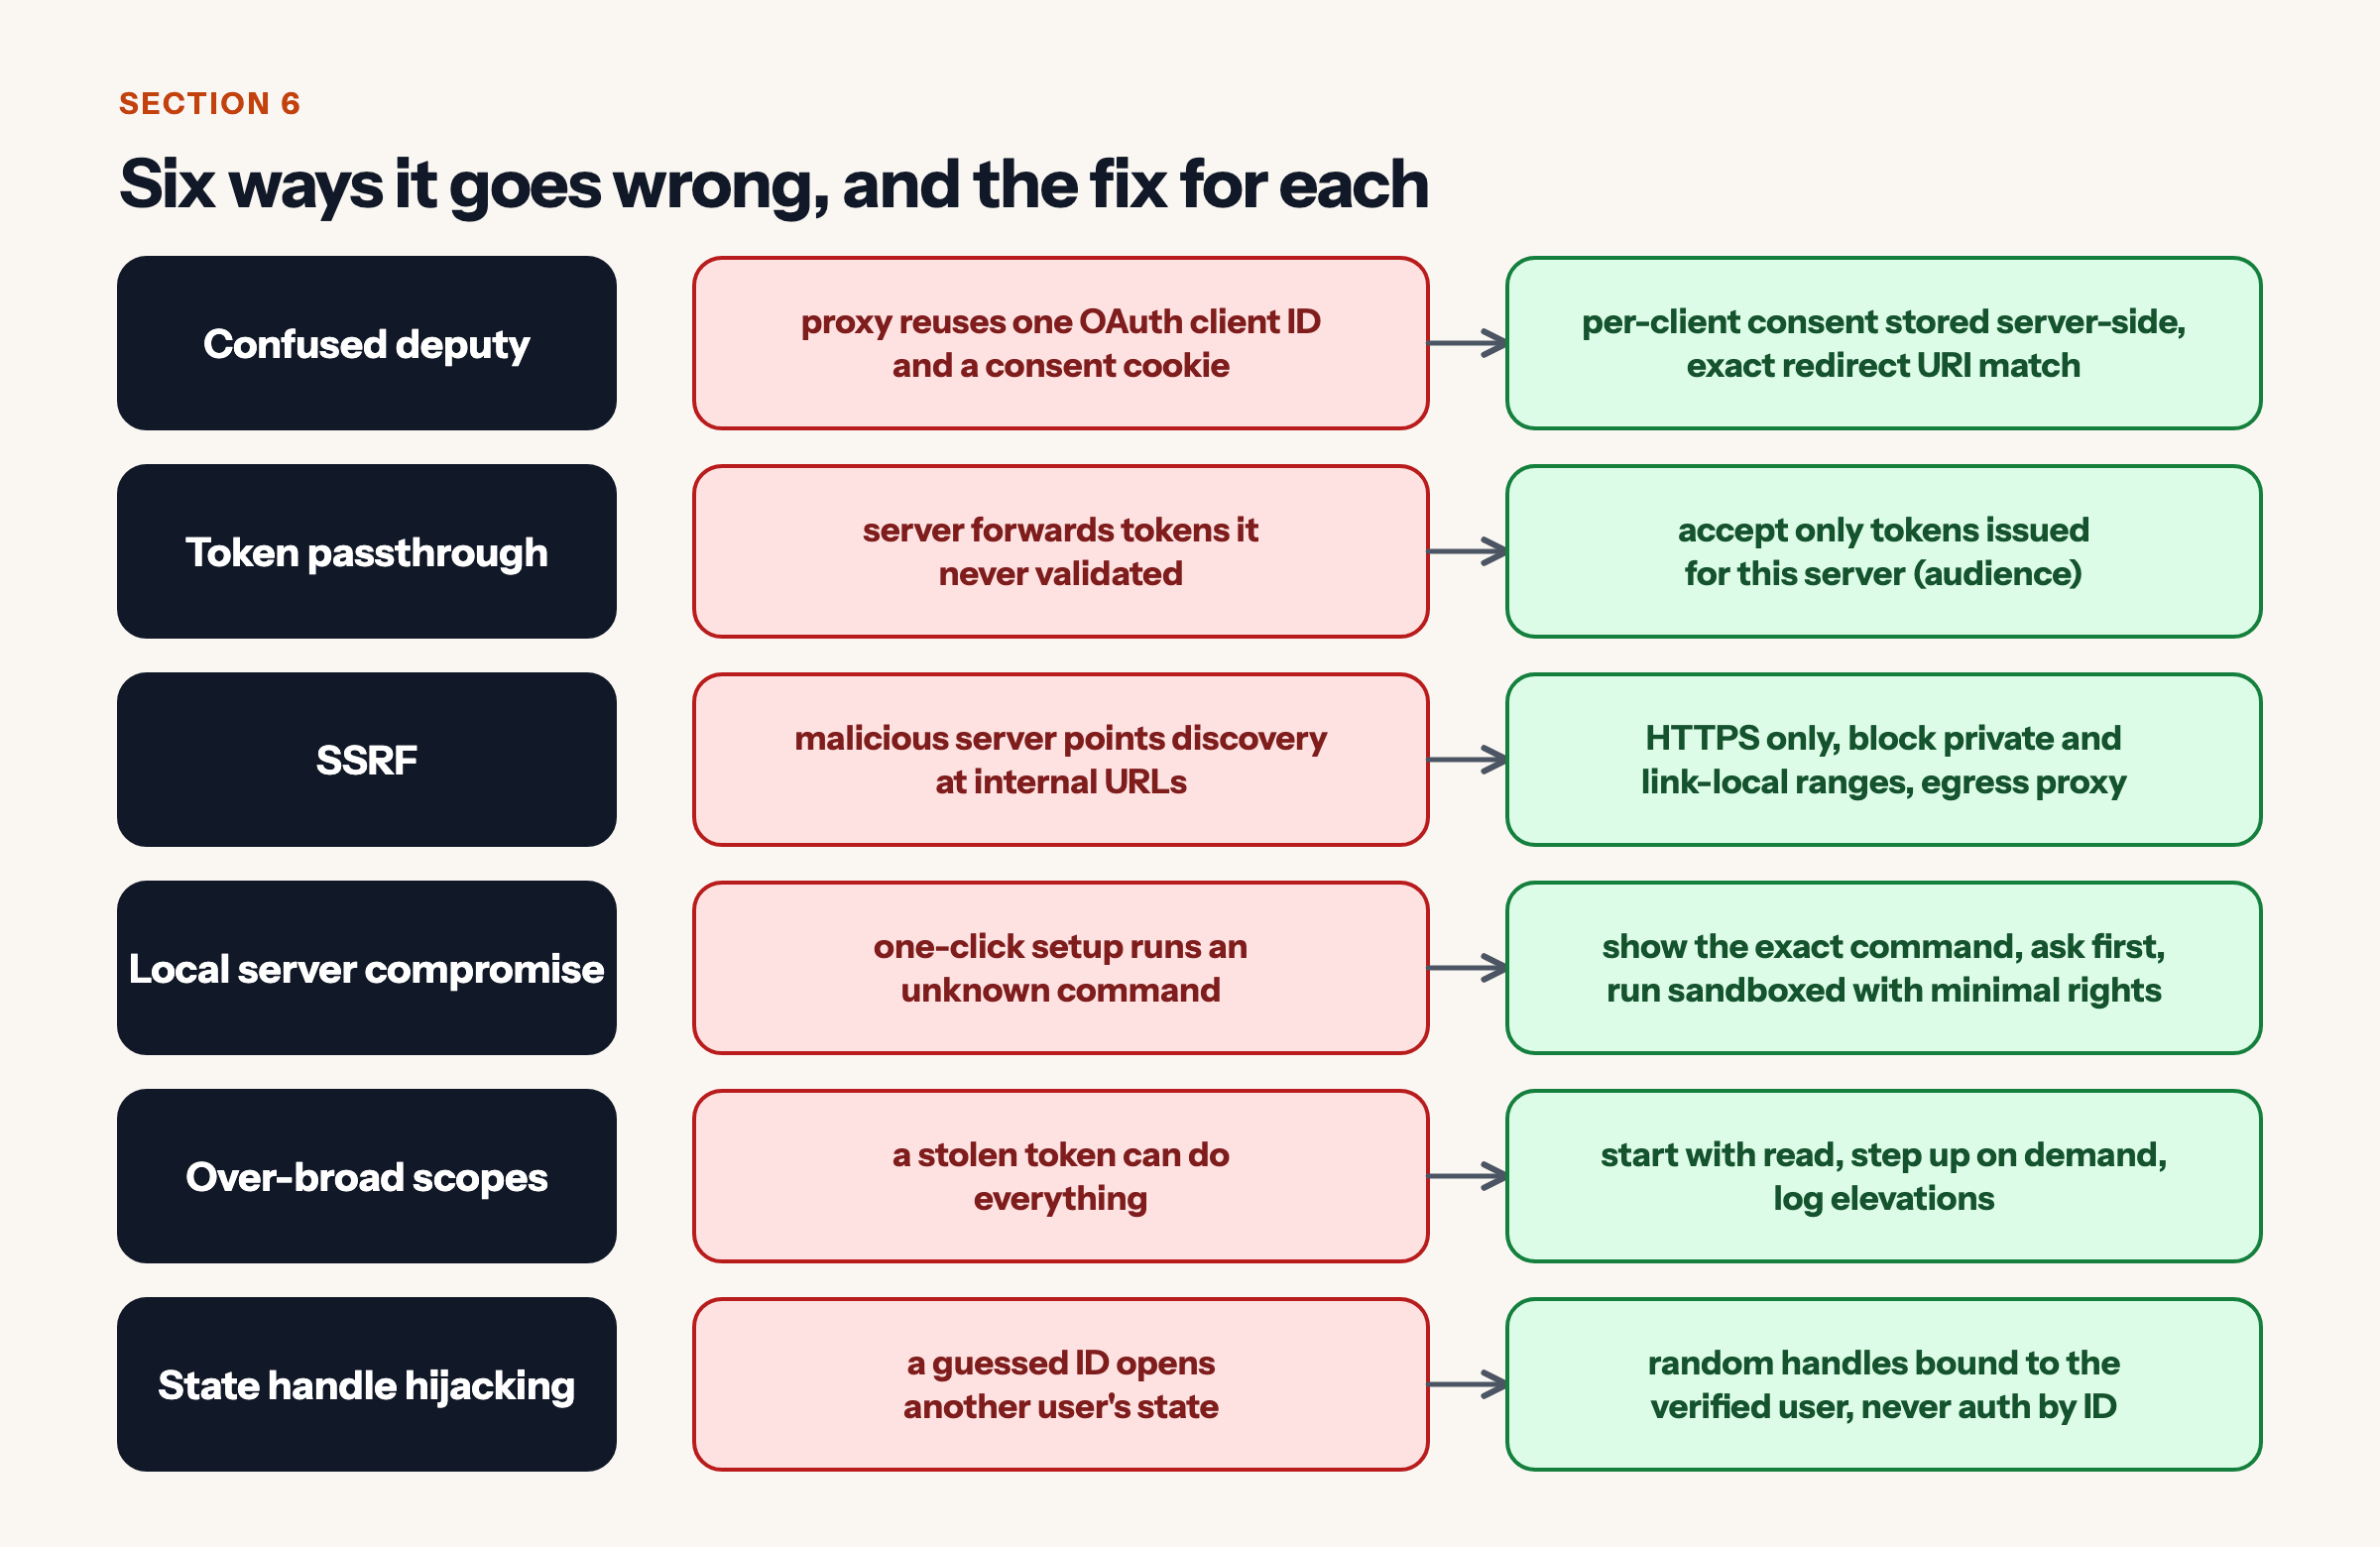
| Risk | What happens | Fix |
|---|---|---|
| Confused deputy | A proxy reuses one OAuth client ID and a consent cookie | Store per-client consent server-side, match redirect URIs exactly |
| Token passthrough | A server forwards tokens it never validated | Accept only tokens issued for this server |
| SSRF | A malicious server points discovery at internal URLs | HTTPS only, block private and link-local ranges, use an egress proxy |
| Local server compromise | One-click setup runs an unknown command | Show the exact command, ask first, sandbox with minimal rights |
| Over-broad scopes | A stolen token can do everything | Start with read, step up on demand, log elevations |
| State handle hijacking | A guessed ID opens another user’s state | Random handles bound to the verified user |
Takeaways
- MCP turns N x M integrations into N + M.
- Host, client, server; stdio locally, Streamable HTTP remotely.
- Tools act, resources inform, prompts template.
- Treat every server as untrusted code with access to your data.
Sources
- Model Context Protocol specification and security best practices (modelcontextprotocol.io).
- OWASP Top 10 for LLM Applications (2025).